-
NCSC Patch Wave: An External Readiness Checklist
NCSC patch wave prep starts outside the firewall: find unknown internet-facing assets, triage likely-affected hosts fast and cut noise. See how.
-
External Attack Surface Management: 9 Costly Errors
External attack surface management fails in practice for nine specific reasons, from narrow seeds to ignored dangling DNS. See the fixes for each.
-
Internet-Facing Asset Inventory: 7 Fields to Record
Build an internet-facing asset inventory that holds up: the 7 fields every record needs, how to confirm candidates and keep it current. See the full list.
-
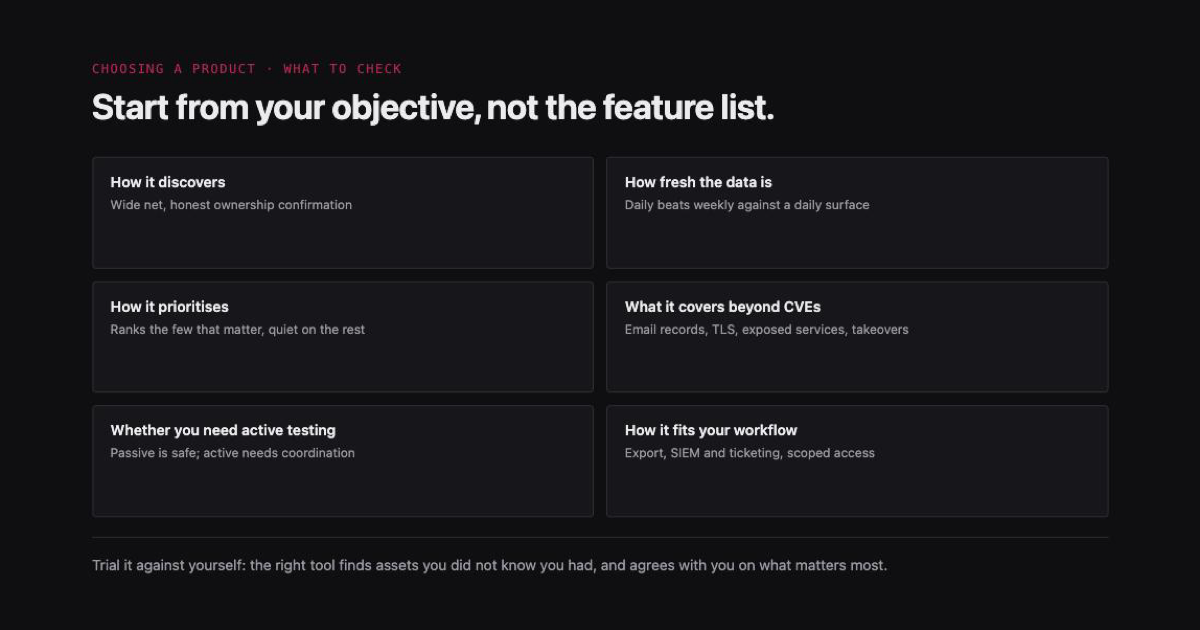
Choosing an EASM Product: A Practical Checklist
Start from your objective, then check how it discovers, how fresh its data is, how it prioritises, what it covers beyond CVEs, whether you need active testing, and…
-
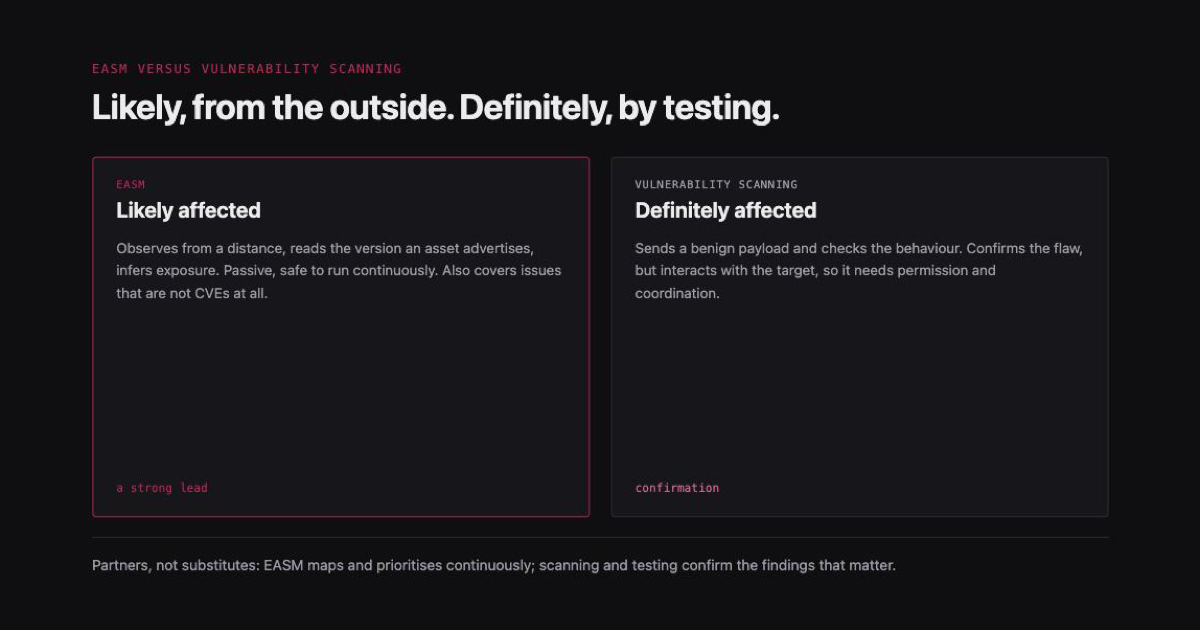
EASM Versus Vulnerability Scanning: Likely Versus Definitely
EASM observes from the outside and tells you a system is likely affected; a scanner tests and tells you whether it definitely is. They are partners, not substitutes.
-
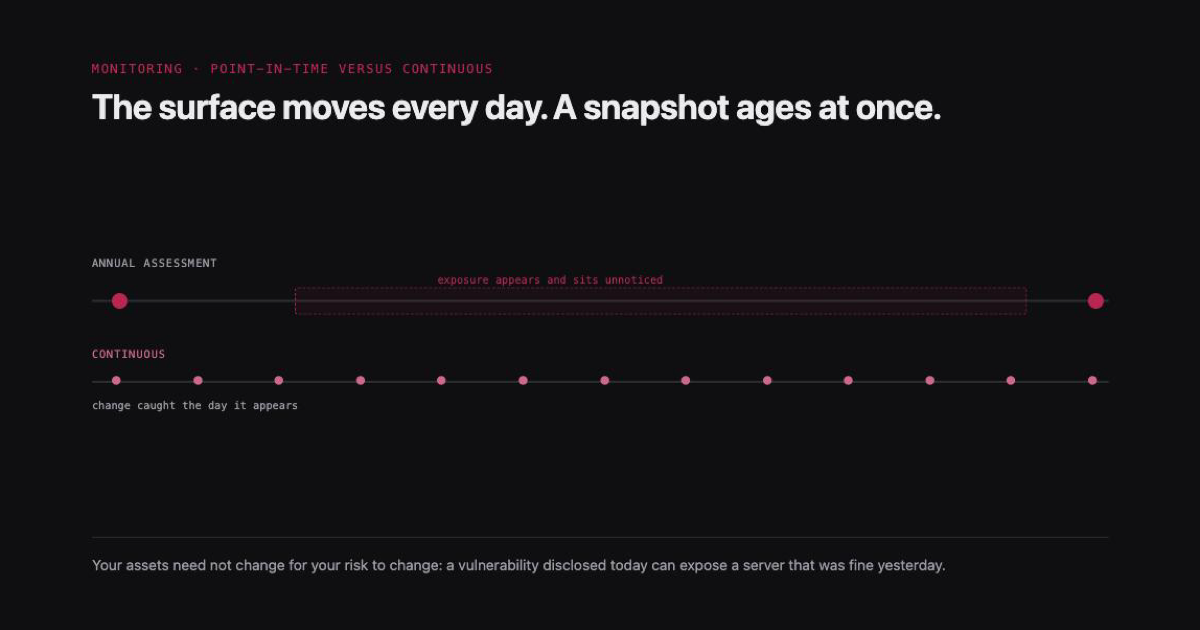
Continuous Monitoring: Why a Point-in-Time Scan Is Not Enough
The external attack surface changes every day, so a snapshot ages at once. Continuous monitoring shows what changed and catches exposure the day it appears.
-
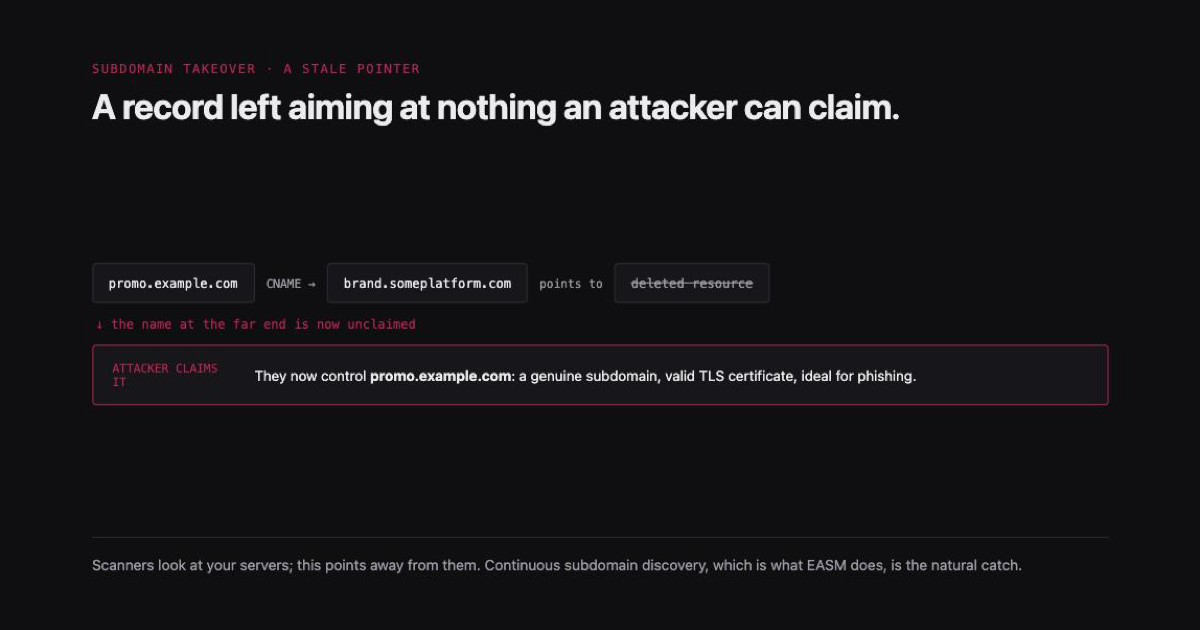
Subdomain Takeover: The Dangling DNS Problem
When a DNS record keeps pointing at a cloud resource after it is gone, an attacker can claim the free name and control a genuine subdomain of your…
-
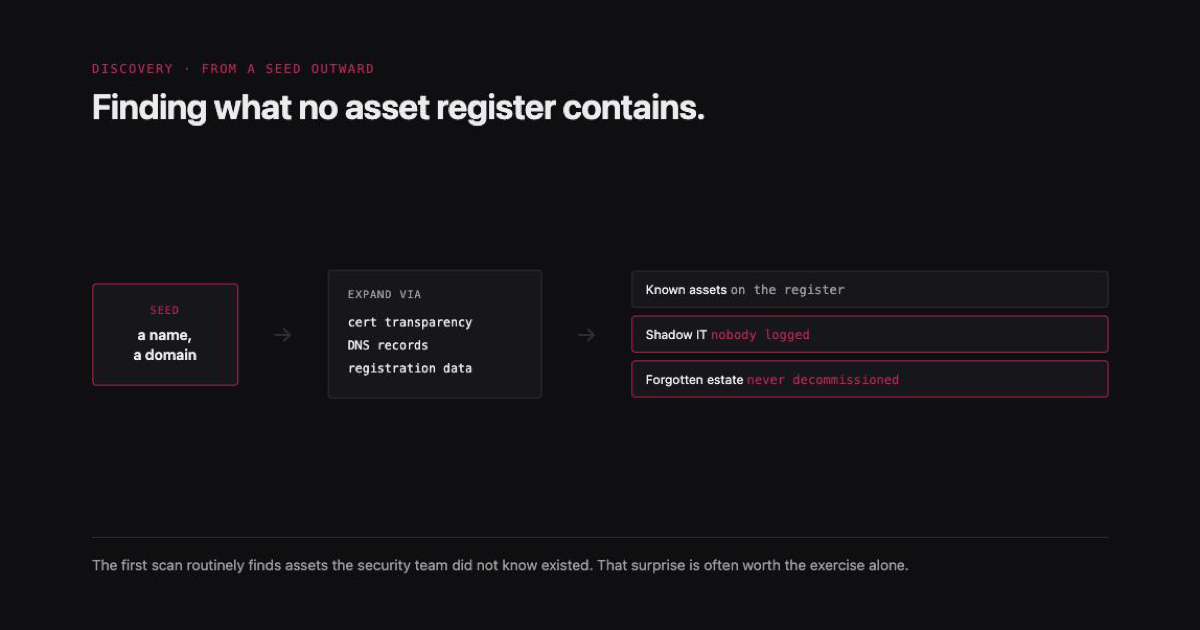
How EASM Discovers the Assets You Forgot
Discovery finds internet-facing assets by expanding from a seed through certificate logs, DNS and registration data, surfacing the shadow IT and forgotten estate no register contains.
-
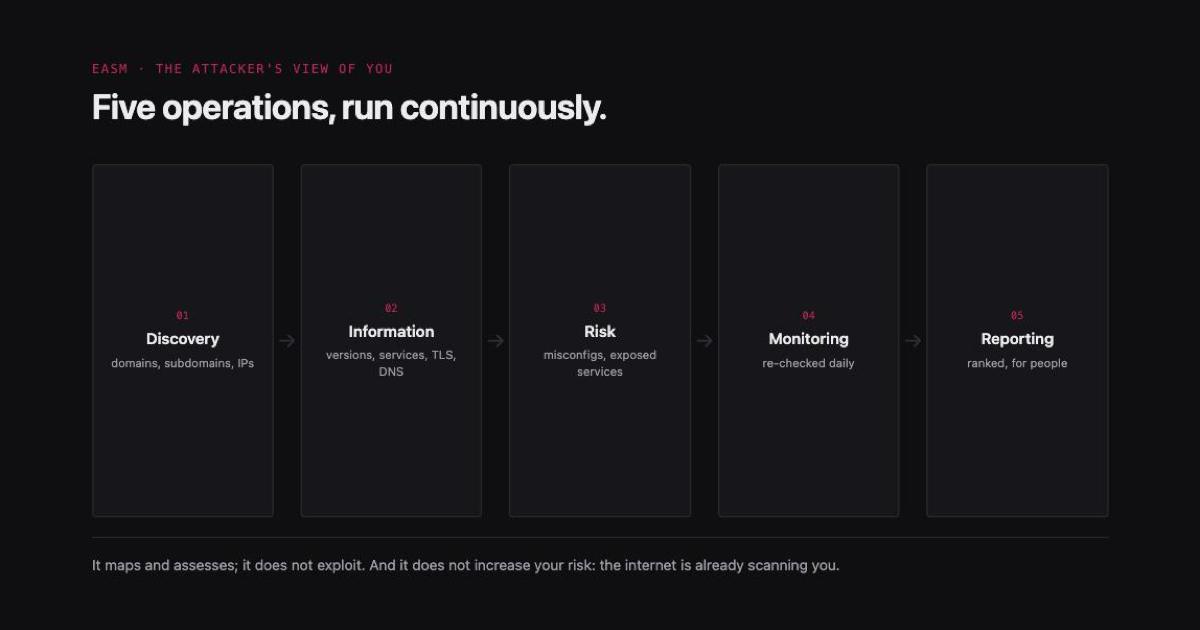
What External Attack Surface Management Actually Is
EASM is looking at your internet-facing assets the way an attacker would, continuously, and fixing what you find. It does not exploit anything, and it does not make…